Rule 791D is the US Commerce Department rule, at 15 C.F.R. Part 791 Subpart D, that bars software and radio hardware with ties to China or Russia from the connectivity and automated driving systems of cars and light trucks sold in the United States. The software ban applies to vehicles from model year 2027 and the hardware ban from model year 2030, and from model year 2027 carmakers owned, controlled or directed by China or Russia may not sell connected vehicles in the US at all. The vehicle maker or importer shows it complies by filing a signed Declaration of Conformity with the Bureau of Industry and Security (BIS) at least 60 days before each model year is imported or sold.
The rule has been in effect since March 17, 2025. The legal text is in the final rule and the current regulation on eCFR. This page covers what the rule asks of you, the dates, and what we see companies doing to meet it.
What Rule 791D covers: connected vehicles, VCS and ADS
Rule 791D doesn't ban everything. It applies to connected vehicles with a gross vehicle weight rating of 10,000 pounds or less, so heavy trucks and most buses are outside it for now. Inside those vehicles, three terms do most of the work:
- Vehicle connectivity system (VCS): hardware or software that sends or receives radio signals above 450 MHz, such as cellular, Wi-Fi, Bluetooth and two-way satellite. Radar, lidar, cameras, ultrawideband key fobs and receive-only signals such as GPS and satellite radio are not VCS.
- Automated driving system (ADS): hardware and software that together can perform the entire driving task on a sustained basis.
- Covered software: application, middleware and system software, with a foreign interest, that runs on the main processors of a VCS or ADS. It excludes firmware that directly controls a hardware device, open-source code unless it was modified for proprietary purposes and not shared back, and software subcomponents made before March 17, 2026 that no China- or Russia-linked party changes afterward.
- China- or Russia-linked manufacturers: a connected vehicle manufacturer owned by, controlled by, or subject to the direction of China or Russia may not sell connected vehicles with VCS hardware or covered software in the US from model year 2027, whoever supplied those parts, and may not offer commercial services in the US that use vehicles with ADS.
Bottom line: if you import or sell a connected vehicle in the US with VCS or ADS features, you must be able to show that the enabling software, and from model year 2030 the connectivity hardware, was not designed, developed, manufactured or supplied by anyone owned by, controlled by, or subject to the direction of China or Russia.
Who files a Declaration of Conformity, and what it says
The connected vehicle manufacturer, the US company that assembles, imports, or integrates ADS software on completed connected vehicles for US sale, answers for covered software. The VCS hardware importer answers for the connectivity hardware it brings in.
Each files a Declaration of Conformity with BIS at least 60 days before the first import or sale of each model year. The CEO, an officer who can bind the company, or an employee one of them designates signs it, and false statements fall under federal false-statement law. The declaration certifies that:
- The covered software or VCS hardware has no China or Russia link as the rule defines it.
- The company did due diligence, with or without third-party assessments.
- It keeps documentation, through a software bill of materials (SBOM) or hardware bill of materials (HBOM) "or otherwise," that BIS can ask for. For software, that means at least the author, timestamp, component name and supplier of every proprietary addition.
- It has taken all possible measures, by contract or otherwise, so suppliers will hand their documentation to BIS on request.
The declaration has to stay true. If you discover an error or omission that could mislead BIS about where the software or hardware came from, you file a revised declaration within 60 days. A software update by itself is not a material change. For a later model year where nothing material changed, a confirmation filed within one year of your last submission can replace a new declaration.
The penalties
Civil penalties go up to the maximum set by the International Emergency Economic Powers Act, adjusted for inflation each year. Willful violations can bring a criminal fine of up to $1,000,000 and, for a person, up to 20 years in prison.
Rule 791D compliance dates
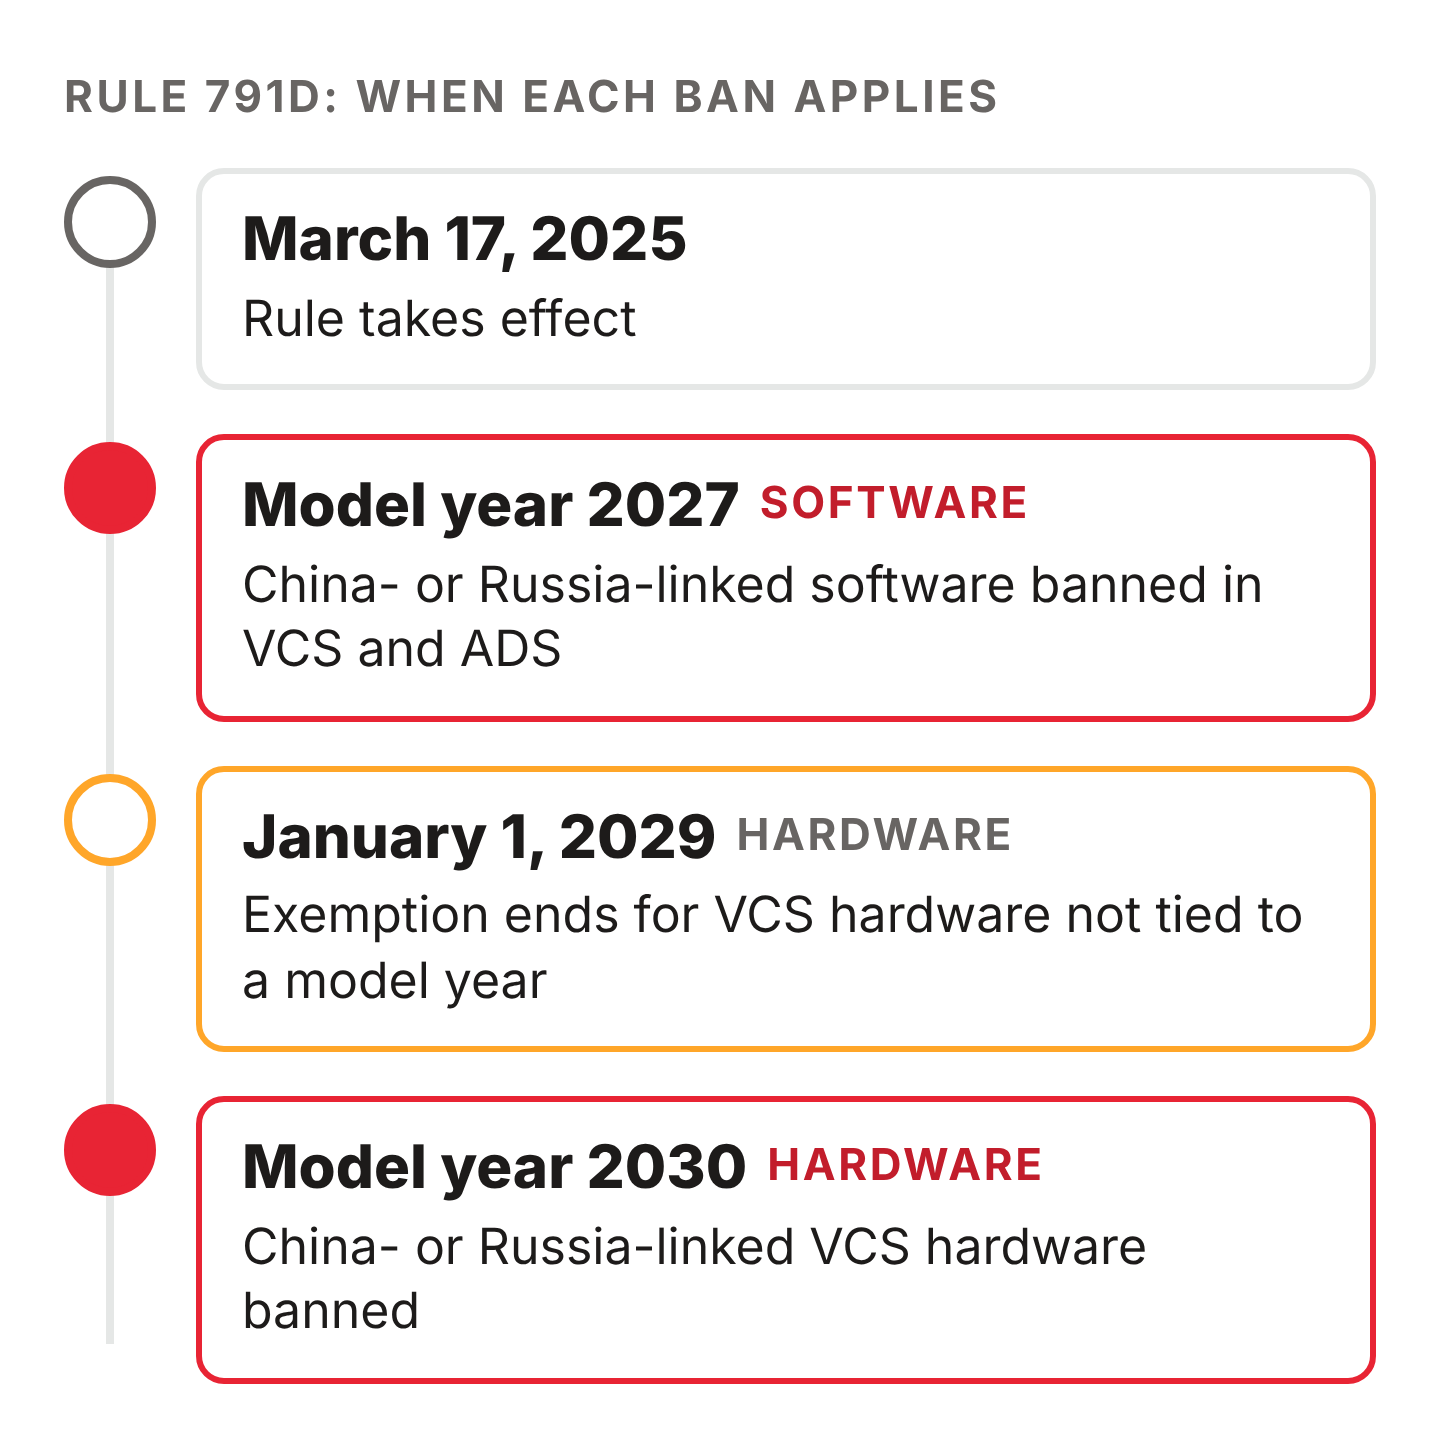
- March 17, 2025: the rule takes effect.
- Model year 2027: the covered software ban applies. Vehicles made before model year 2027 are exempt.
- January 1, 2029: VCS hardware not tied to a model year stays exempt only if imported before this date.
- Model year 2030: the VCS hardware ban applies. Hardware for earlier model years, including repair and warranty parts, stays exempt.
Why does software come first?
Every connected vehicle carries VCS hardware, so it can look odd that China-linked hardware may still go into pre-2030 vehicles while the software is cut off from model year 2027. Our read: software can be updated remotely and changed after sale, so it is the faster-moving risk, while hardware is locked into long design cycles and takes longer to replace. For model years 2027 through 2029, the hardware may still come from a restricted source, but the software running it has to be clean.
Exceptions: general and specific authorizations
General authorizations are pre-cleared cases you can use without applying, as long as you meet their terms and keep records for 10 years. BIS lists three on its general authorizations page:
- No. 1, Limited Use Cases (amended June 18, 2026): testing on public roads fewer than 30 days in any 12 months, display, testing or research vehicles, and temporary imports for repair, alteration or competition that leave within a year.
- No. 2, Temporary Importation (amended November 19, 2025).
- No. 3, Approved Supplier Registry (June 18, 2026): a supplier applies with a risk proposal for its own products. Once listed, manufacturers and importers can use those products without a specific authorization, but they still file their own declarations. BIS has not published the registry yet.
Specific authorizations cover everything else. You apply to BIS and describe the security standards you use, your technical and operational controls, and how you limit Chinese or Russian government access; BIS aims to decide within 90 days (specific authorizations page). In our view, an ISO/SAE 21434-aligned TARA (threat analysis and risk assessment), secure design validation, limited remote access and tamper-evident logging are the kind of evidence this path needs. It is a high bar.
Where supplier attestation falls short
Some original equipment manufacturers (OEMs), the vehicle makers, will ask suppliers to sign statements that mirror the Declaration of Conformity, but the declaration is still the OEM's to sign. Most compliance work today falls into three buckets:
- Tighter supplier due diligence: new onboarding forms, updated cybersecurity interface agreements and sharper sourcing questions.
- Deeper threat assessments: if your TARA ends at Tier 1, it ends too early. Where software is written and where chips are made now matter.
- Surveys and spreadsheets: these work only if the people filling them out know where their subcomponents come from, and they often don't.
Even honest answers can miss. In our work, a supplier attested in good faith that its module had no Chinese code in use. A scan of the firmware found Chinese code in the image: the module is sold worldwide, and a region setting switches that code on only for the China market. "Not active" answered a different question from the one the declaration certifies, and the OEM had the code removed. It is the country-of-origin version of the problem we covered in Securing the Automotive Supply Chain.
How Block Harbor helps with Declarations of Conformity
Our VSEC platform tracks cybersecurity risk across the development lifecycle, and for Rule 791D it lets you:
- Keep the evidence in one place: supplier letters, surveys, TARAs, SBOMs and HBOMs, attached to the component they describe.
- Check firmware against what suppliers declared: a partner's binary scanner builds an SBOM from the firmware, even when the supplier didn't share one, and tags where each package comes from. VSEC stores the findings as risks on that component and flags where declared and detected answers disagree.
- Record which firmware is on which vehicle program and export the reports behind each declaration.
Expect hand work: firmware comes in many non-standard formats, and so far most images have needed manual reverse engineering before they give up their contents. Our lab also extracts SBOM and HBOM data from VCS and ADS components when a supplier can't or won't. More on that in Know the "Where" of your Firmware.
What you should do now
If you already write ISO/SAE 21434 requirements into your requests for proposal (RFPs), add requirements aligned with Rule 791D so suppliers know what evidence you will ask for before the project starts. Revise supplier agreements and cybersecurity interface agreements to ask where software and hardware are designed and built. Then plan how you will check supplier surveys, SBOMs and HBOMs against the components and firmware you actually receive.
Two things to watch. BIS plans a separate rule for medium- and heavy-duty vehicles, listed in the July 2026 regulatory agenda as a long-term action with no date (here is what a truck maker would have to sign). And the Connected Vehicle Security Act, a bill that would write a similar ban into law, passed the Senate Commerce Committee in July 2026 and is not law yet.
If you are building your first Declaration of Conformity, or your supplier answers and your firmware don't line up, talk to us. Bring one component or one vehicle program, and we'll walk through what the evidence behind it would look like.
Subject expert

Dustin Mills is Director of Product Cybersecurity Engineering & Operations at Block Harbor, where he leads end-to-end engagements with OEMs and suppliers that secure connected vehicles across their lifecycle. He's at his best when working on ambiguous problems that span multiple teams.