
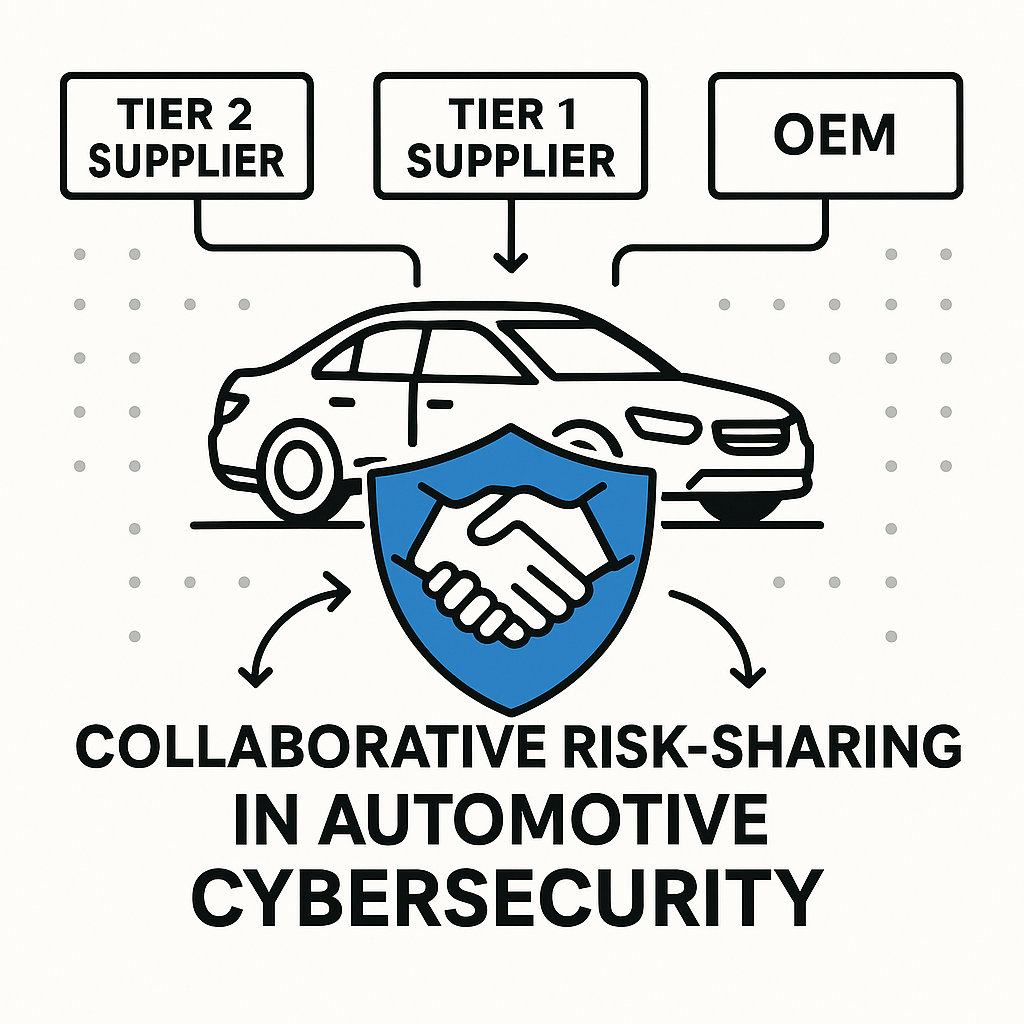
Collaborative Risk-Sharing in Automotive Cybersecurity
Presented at ESCAR USA 2025 by Atefeh Asayesh
As modern vehicles become more connected and software-driven, cybersecurity threats no longer stop at organizational boundaries. Vulnerabilities in Tier 2 supplier components can propagate to Tier 1 supplier systems and all the way to the OEM — yet today’s TARA practices treat these risks in silos.
At ESCAR USA 2025, we introduced a Collaborative Risk-Sharing Framework that addresses this challenge by quantifying shared cybersecurity responsibility across the automotive supply chain.
What’s the Problem?
- ISO/SAE 21434 mentions risk sharing — but provides no technical and practical method to do it.
- Suppliers’ risks often remain hidden or misassigned.
- There’s no consistent way to allocate mitigation responsibility or measure impact reduction efforts across stakeholders (cf. Figure 1). This can lead to a breach as described in Table 1.


Our Proposed Solution
We developed a multi-step framework that enhances standard TARA by:
- Modeling weighted, multi-dimensional impacts across safety, privacy, finance, and operations.
- Applying stakeholder-specific mitigation factors to both impact and feasibility.
- Calculating final residual risk using an extended formula aligned with ALARP (As Low As Reasonably Practicable) principles.
- Clarifying ownership of shared risks and enabling defensible decision-making.
Note: We also recommend introducing a simple Cyber Risk Contract between stakeholders to clearly define roles, responsibilities, and expectations for cybersecurity ownership throughout the supply chain. Our proposed solution is summarized in Figure 2.

Who Benefits?
- OEMs gain better insight into inherited supplier risks and can act accordingly.
- Tier 1 and Tier 2 suppliers can demonstrate proactive risk reduction.
- Auditors and insurers can assess how well risks are being managed collaboratively — before a breach happens.
Download the full paper
Stay Connected with Block Harbor
Keep up with the latest in vehicle cybersecurity through our specialized newsletters. Choose the option that best fits your interests and role.
Thank you for your submission!
Read More
Explore more automotive cybersecurity insights from our experts. Discover best practices, case studies, and emerging trends to strengthen your organization's security posture.
Building a VSOC for an EV fleet taught us to pick monitoring use cases first, then check the data against them and turn gaps into engineering requirements.
A pen test describes one build. Turn each finding into a test case that re-runs on the real ECU every release, and the evidence outlives the report.
A managed bug bounty platform is the last purchase in a disclosure program. FIRST's PSIRT maturity levels show what to build first and when a platform pays.
AI TARA tools automate the analysis half. The item definition they need first is where your hours go, and most programs cannot hand them one.
Try Block Harbor Today
Start protecting your vehicles with the same platform the world’s best hackers and defenders use.


